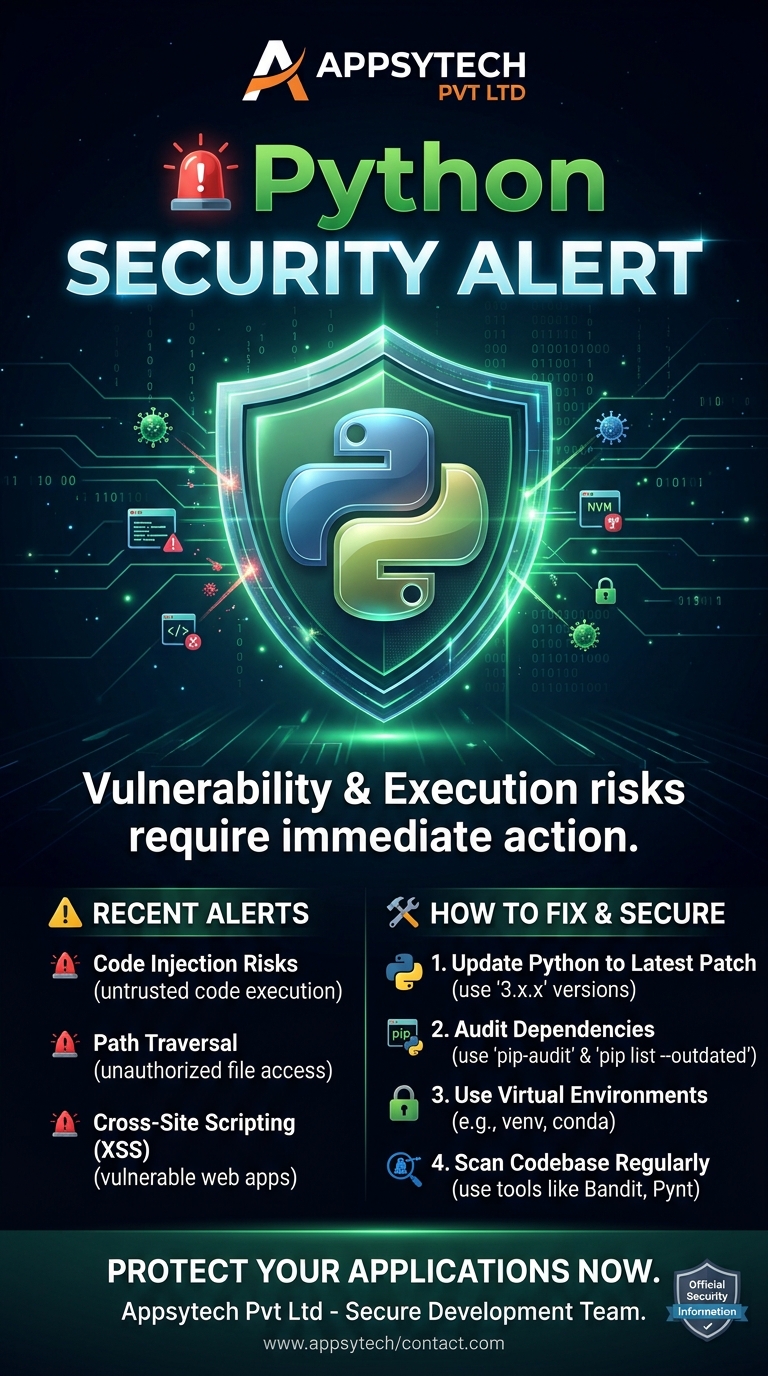
🐍 BREAKING: Python Software Foundation Flags Critical Core Vulnerabilities
Title: Python Security Alert: Core Library Patches Address SSL & File Parsing CVEs
Summary:
The Python Software Foundation (PSF) and CPython security team have released critical security advisories addressing multiple vulnerabilities spanning CPython standard modules.
Key Highlights:
- SSL/TLS Validation Flaws: High-severity advisories highlight missing hostname checks and memory allocation race conditions in
SSLContextmodules. - File System & Extraction Vulnerabilities: Patches address critical filters in
tarfileand archive utilities that previously allowed path traversal and unauthorized file overwrites. - Resource Exhaustion: Fixes resolve super-linear CPU utilization and unbound decompression bounds across standard data modules.
🛠️ How to Fix:
- Upgrade Python Runtime:
- Update your system interpreter to the latest patch release (e.g., Python 3.11+, 3.12+, or 3.13+):
Bash sudo apt-get updatesudo apt-get install --only-upgrade python3
- Scan Package Dependencies for CVEs:
- Install and run
pip-auditto inspect your project'srequirements.txtor active virtual environment for known vulnerable packages:
Bash pip install pip-auditpip-audit -r requirements.txt
- Safeguard Archive Extractions & Secure Code Patterns:
- If using standard archive parsing routines like
tarfile, apply safer extraction flags or explicit path checks: - Python
# Python 3.12+ safe extraction usageimport tarfilewith tarfile.open("archive.tar") as tar: tar.extractall(path="./destination", filter="data")
Have a perspective or question about this article?
Comments (0)
No comments yet. Be the first to share your thoughts.