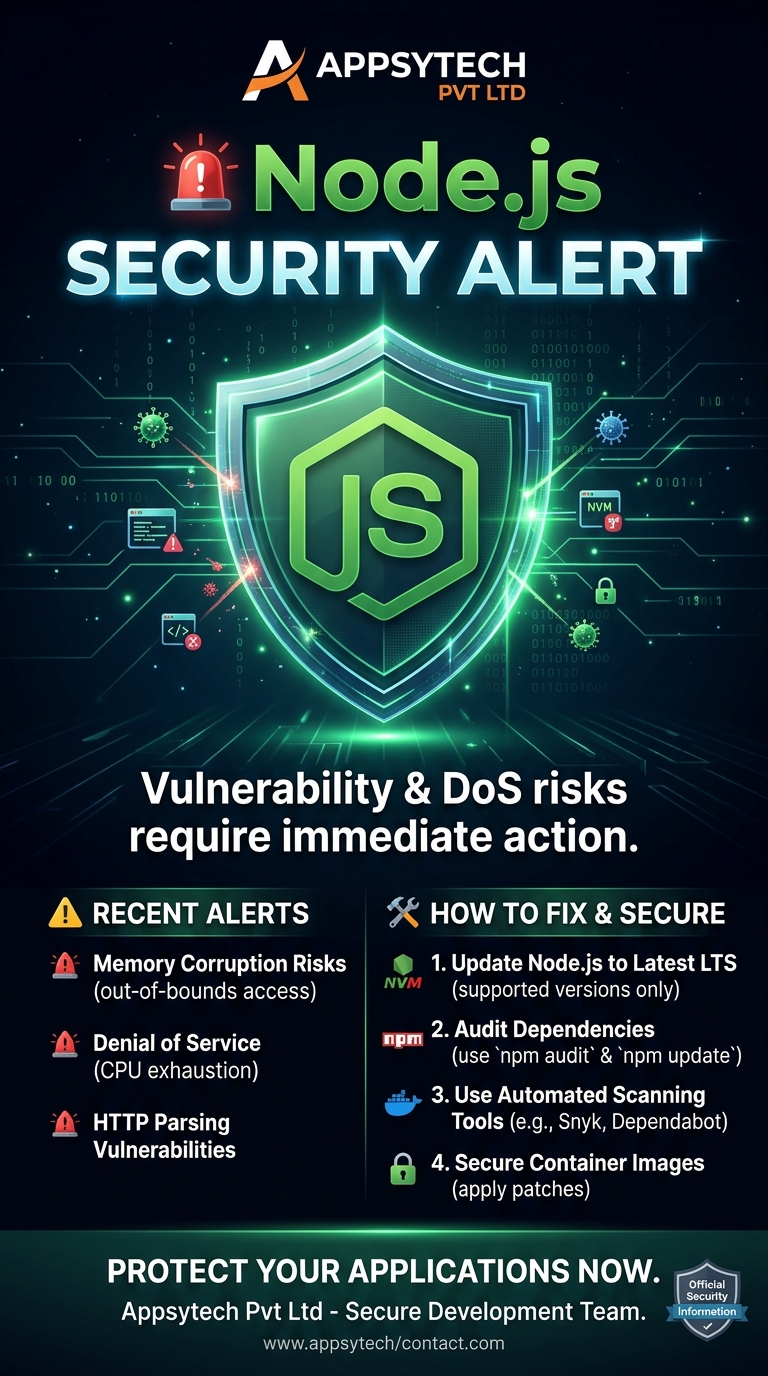
🚨 BREAKING: Security Advisory Issued for Node.js Runtimes
Title: Node.js Security Release: Critical Patches Address Memory Corruption & DoS Flaws
Summary:
The Node.js Project Security Team has issued an emergency release batch addressing high-severity security vulnerabilities across multiple active Release Lines. Organizations running production Node.js services are urged to upgrade immediately.
Key Highlights:
- Memory Corruption Risks: Patches address critical out-of-bounds array access and memory management flaws within core processing modules, preventing arbitrary code execution.
- Denial of Service (DoS): Fixes mitigate CPU-exhaustion vulnerabilities in HTTP request parsers and stream processing interfaces.
- Affected Versions: Older Node.js releases prior to recent patch versions.
🛠️ How to Fix:
- Update Local & Production Runtimes:
- If using NVM (Node Version Manager):
- Bash
nvm install --ltsnvm use --lts
- If on Ubuntu / Debian:
Bash sudo apt-get updatesudo apt-get install --only-upgrade nodejs
- Audit and Update Dependencies:
- Run the built-in vulnerability scanner to find and automatically fix high-severity package risks:
Bash audit fix
- Rebuild Container Images & Restart Services:
- Pull the updated official Docker base image (e.g.,
node:22-alpineor your target LTS tag) in your Dockerfile and trigger a redeploy: - Bash
docker build --no-cache -t my-app .
Have a perspective or question about this article?
Comments (1)
Thanks for sharing your solution