PHP Foundation Issues Mitigation Advisory for Session RCE Vectors
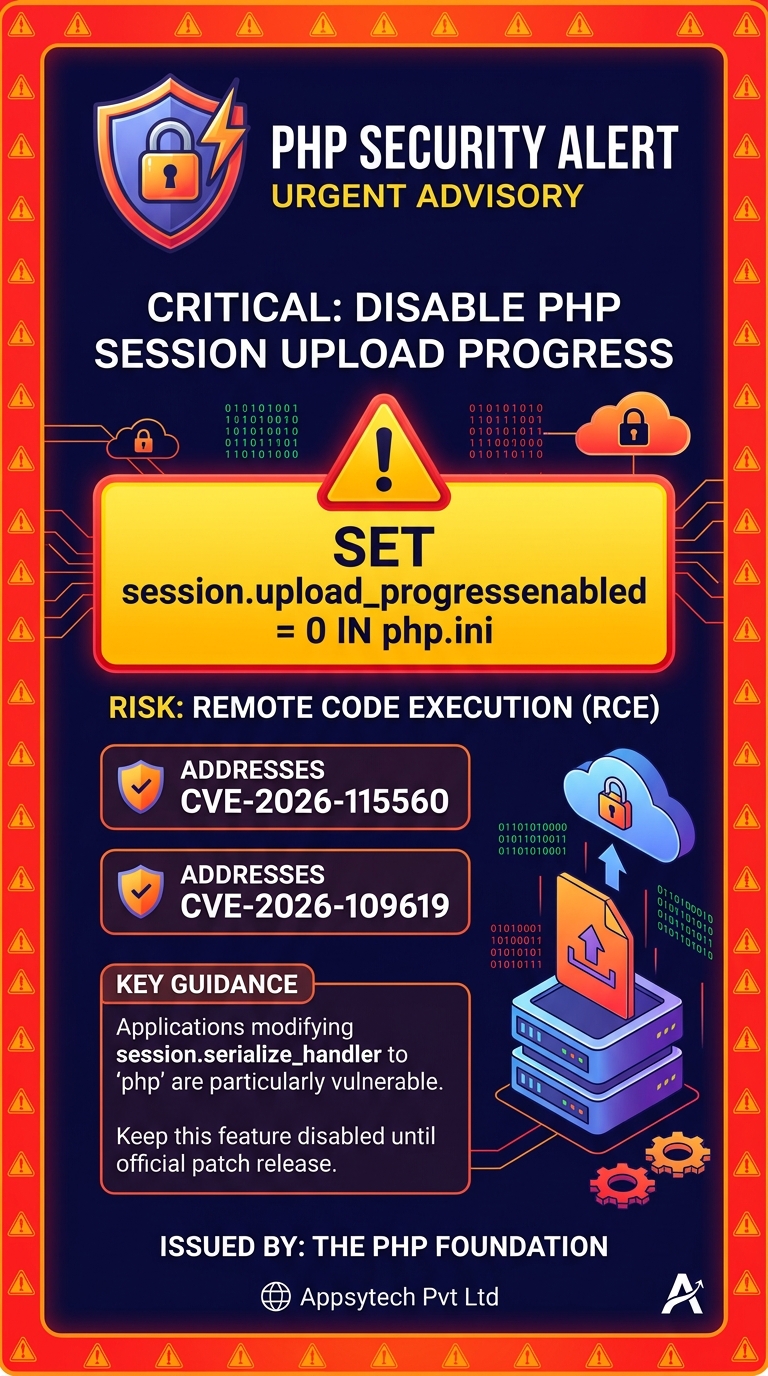
The PHP Foundation has issued an urgent security notice advising organizations to set session.upload_progress.enabled=0 in their php.ini configuration. The measure addresses Remote Code Execution (RCE) vectors identified under CVE-2026-115560 and CVE-2026-109619.
The risk applies primarily to applications executing runtime modifications to session.serialize_handler (specifically switching to "php"). System administrators are urged to maintain this feature disabled until the release of the upcoming official PHP patch.
Appsytech Pvt Ltd
Have a perspective or question about this article?
Comments (1)
Appreciate it sir