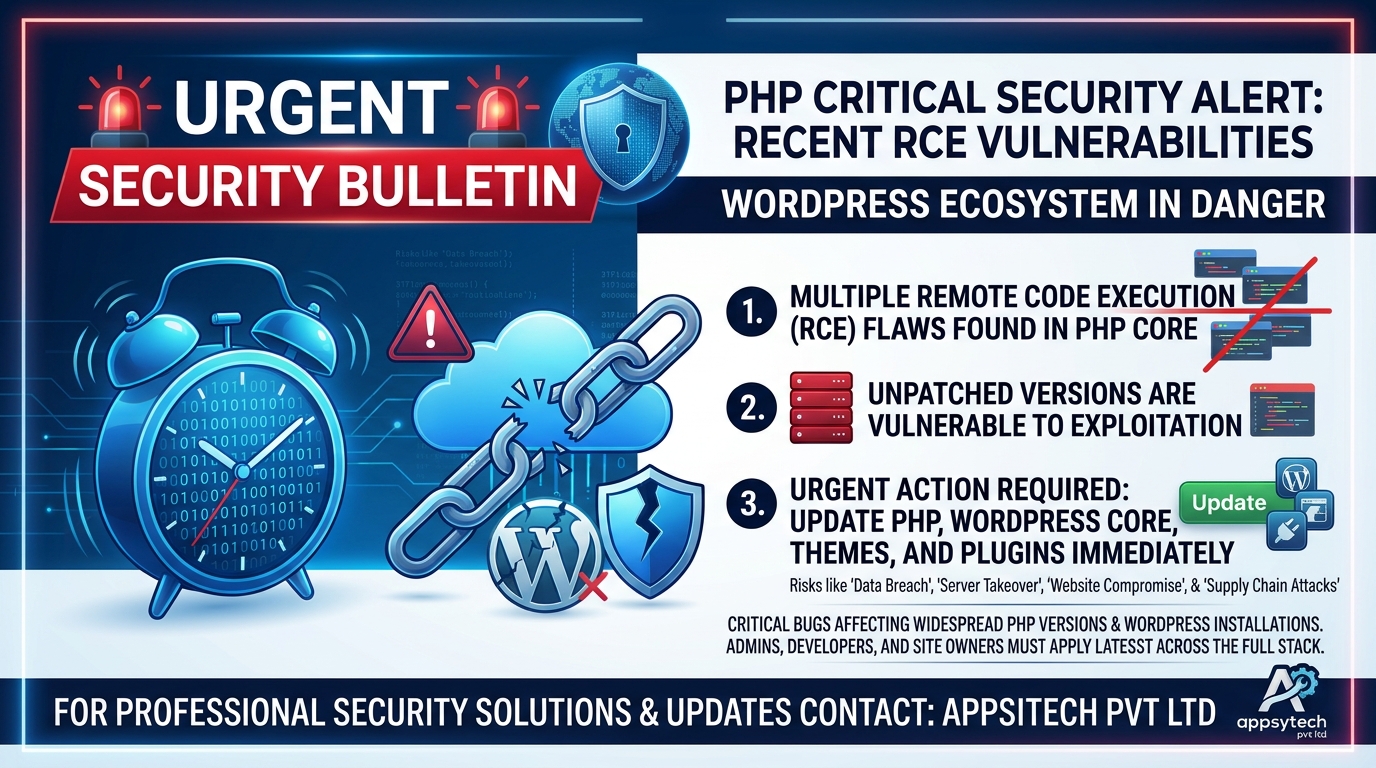
🚨 URGENT SECURITY ALERT FOR ALL WEBSITE OWNERS & DEVELOPERS 🚨
A critical security vulnerability—PHP2Shell (CVE-2026-109618 & CVE-2026-109619)—has just been uncovered in the core engine of PHP!
If your website runs on PHP or WordPress, your server could be at immediate risk of unauthenticated Remote Code Execution (RCE)—allowing cybercriminals to take control of your server without needing a login.
🔍 What You Need to Know:
💣 The Bug: Unauthenticated Remote Code Execution (RCE) in the PHP core engine.
🌐 Who is Affected? All unpatched PHP versions (8.1 and earlier, as well as unupdated releases of 8.2, 8.3, 8.4, and 8.5).
⚠️ WordPress Impact: Updating WordPress plugins or themes WILL NOT fix this! Because this is a core server issue, your entire hosting environment must be patched.
⚡ The Threat: Server takeovers, data breaches, database dumps, defacement, and malicious backdoors.
🛡️ Immediate Action Required:
Check your PHP version immediately via your control panel or php -v.
Upgrade to safe patch releases:
PHP 8.5 ➔ Update to 8.5.12+
PHP 8.4 ➔ Update to 8.4.27+
PHP 8.3 ➔ Update to 8.3.36+
PHP 8.2 ➔ Update to 8.2.35+
If running PHP 8.1 or older (EOL), migrate to a supported version right away.
💡 Need expert assistance securing your digital infrastructure?
Don't wait for a breach to happen. Get in touch with our team of security professionals today!
📞 Contact Appsytech Pvt Ltd for complete security audits, PHP upgrades, and server hardening solutions.
#CyberSecurity #PHP #WordPressSecurity #PHP2Shell #InfoSec #ServerSecurity #Appsytech #TechAlert #WebDevelopment #DataProtection
Have a perspective or question about this article?
Comments (1)
its perfect information, thanks sir